Static Inbound and Outbound IP Options for Pantheon Sites

The missing network layer for WebOps.

Connect WordPress and Drupal to IP-restricted APIs, banking gateways, and supported legacy services. Start with the application client making the request, then choose the right static IP route.

Diagram showing two servers connected to a secure shield with a lock icon and a calendar interface inside the shield, labeled Pantheon.

Enterprise Connectivity for WebOps

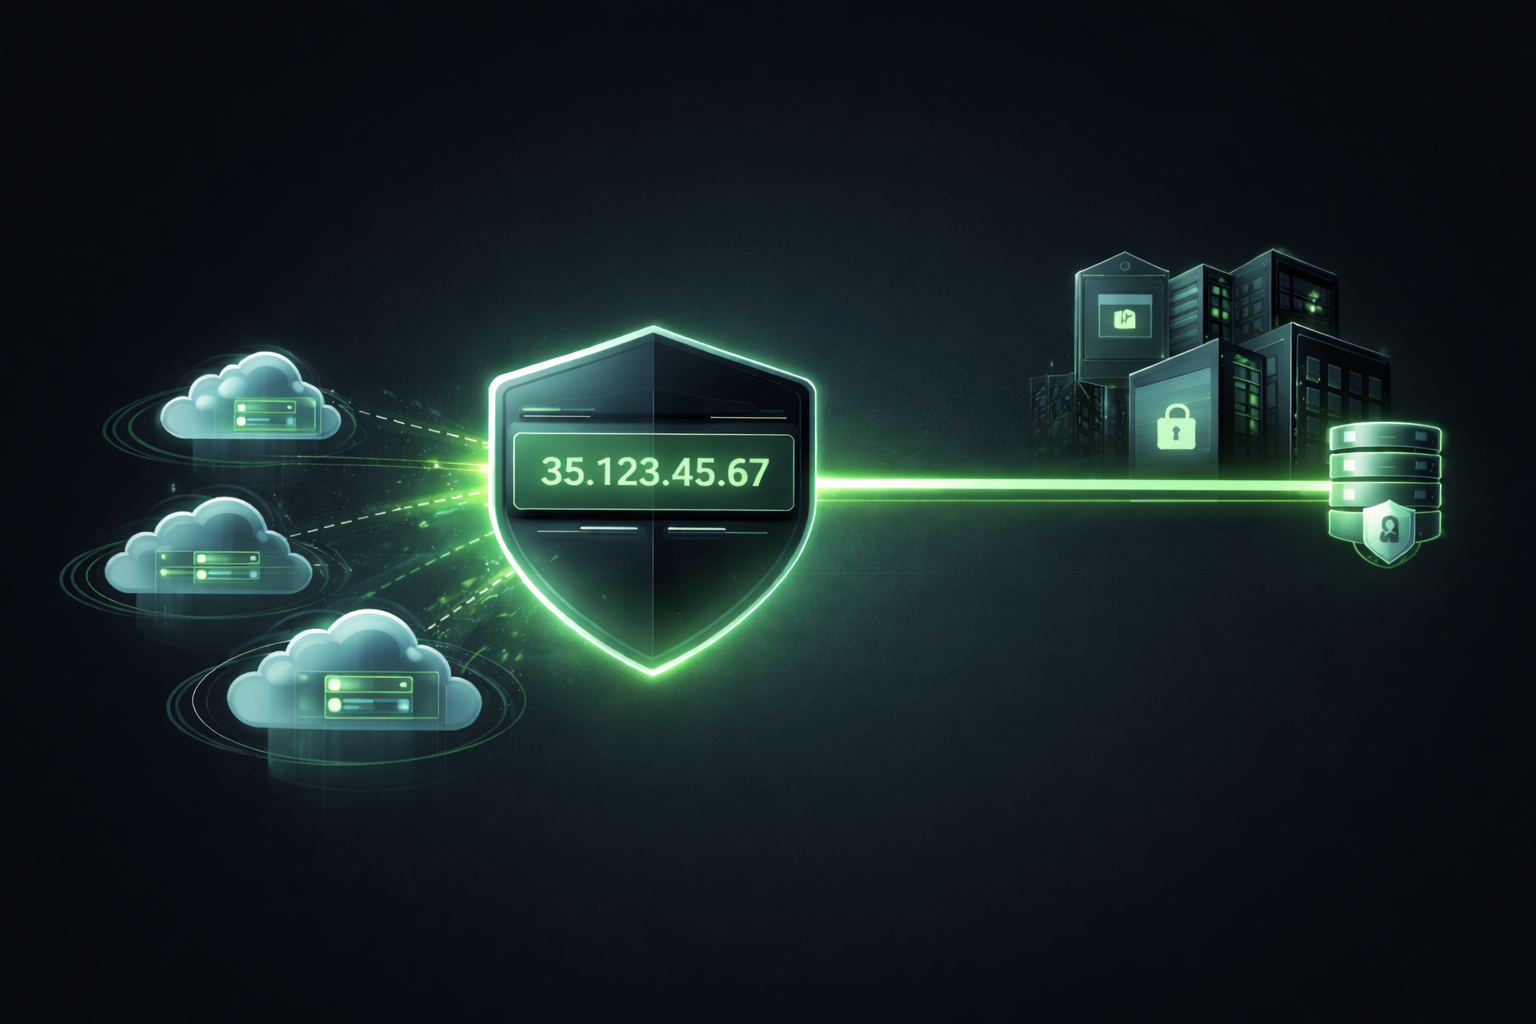
Give supported WordPress and Drupal requests stable source IPs for partner allowlists, without moving your site off Pantheon.

Configure the actual outbound client. Inbound connectivity uses a separate reverse-proxy setup; our engineers can help you choose the route.

Note: Designed for backend connectivity (SQL, SOAP, APIs). This solution is not intended for web scraping consumer sites (e.g., social media or ticketing platforms) that block cloud infrastructure.

Native Outbound Configuration

For a headless Drupal site or a WordPress WooCommerce store, start with the client making the request. Does it support an HTTP proxy for Static or an HTTPS proxy for Shield? Both preserve destination HTTPS; Shield also encrypts the proxy hop.

We run the proxy service. Your team configures clients, protects credentials, handles errors, and arranges allowlisting of both IPs. Pantheon manages the runtime. Follow the Pantheon integration guide for client recipes and setup details.

WordPress Config

Standard WordPress proxy constants configure the WordPress HTTP API’s proxy path, subject to bypass rules, filters, and transport support. They do not configure every plugin, SDK, independent cURL client, or native connection. Use the documented Static recipe for these constants. For Shield, use an explicitly configured HTTPS-proxy-capable cURL or Guzzle client, or a separately validated WordPress transport integration; changing the port alone is not enough.

Drupal Settings

Drupal’s $settings['http_client_config'] applies to clients created through Drupal’s HTTP client factory. Independent Guzzle clients have their own settings, and client or request options can override factory defaults. For selected integrations or Shield, use a dedicated compatible client with an explicit handler and proxy configuration, preserving Drupal’s existing shared-client middleware.

Secure Tunneling (SOCKS5)

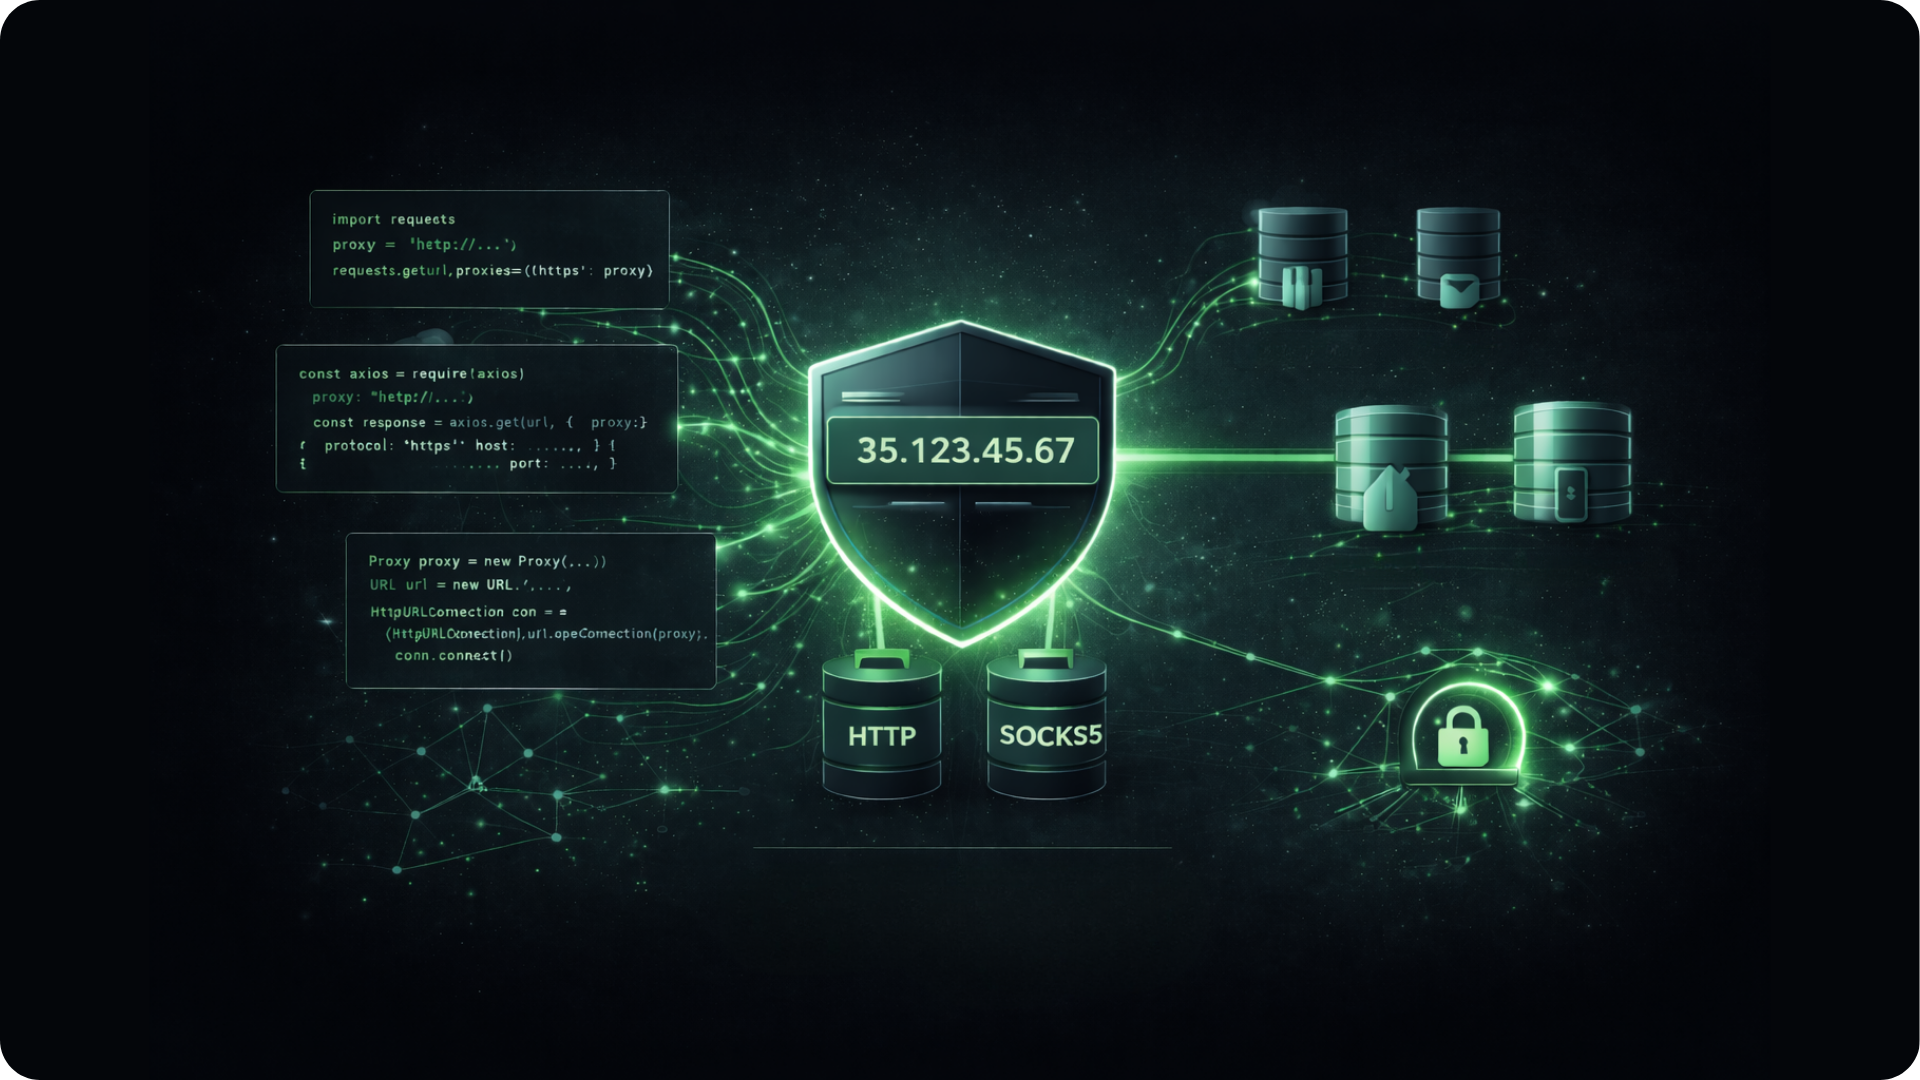
SOCKS5 is an option when the requesting client supports it. Native database, LDAP, and SFTP clients need their own transport configuration; they do not inherit CMS HTTP settings. QGTunnel is not an available installation path on Pantheon. Check the client’s supported proxy or tunnel options before selecting this route, or discuss a separate managed tunnel or HTTPS service architecture.

Digital shield with IP address 35.123.45.67 connected to HTTP and SOCKS5 proxies and cloud storage icons with encryption lock.

Built for WebOps & Agencies

We understand the agency workflow. You have Dev, Test, and Live environments.

QuotaGuard works across your entire Pantheon workflow, allowing you to test connectivity in a sandbox before deploying the static IP configuration to production.

FAQs

Specifics on configuring wp-config.php, settings.php, and handling environment variables for your Pantheon Static IP.

Can I use QuotaGuard to connect my Pantheon site to an external Microsoft SQL Server?

Possibly, depending on the installed runtime, driver, and supported network path.

Pantheon documents SQL Server extensions in its newer PHP runtime, so the absence of system-level installation access does not mean all direct SQL connections are impossible.

However, WordPress or Drupal HTTP proxy settings do not configure PDO_SQLSRV, and that driver has no documented proxy connection option. Assess the actual driver and an appropriate tunnel, Pantheon Secure Integration, or an authenticated HTTPS service.

Do not assume a SOCKS5 subscription alone configures the SQL client.

Does modifying wp-config.php route all my WordPress traffic through the proxy?

No.

The standard constants apply to requests using WordPress’s HTTP API and its proxy decision, subject to its transport, filters, and bypass rules. Independent SDKs and native clients need separate configuration.

Use WP_PROXY_BYPASS_HOSTS for destinations that do not need static IPs, such as wordpress.org updates, so those requests do not consume proxy bandwidth. Keep protected destinations out of the bypass list. Check each gateway or plugin’s actual client rather than assuming it inherits the settings.

The standard constants are not a portable Shield configuration.

How do I handle different credentials for Dev, Test, and Live environments?

Use Pantheon Secrets with environment overrides. Pantheon currently makes Secrets available to all users.

For website PHP requests, create the secret with runtime type and web scope and retrieve it with pantheon_get_secret; Secrets are not automatically ordinary environment variables.

Account for Pantheon’s documented server cache when rotating a value. Keep credentials out of committed code, URLs printed to users, and raw error logs.

Pantheon documents the same web-scope retrieval requirements for Quicksilver scripts.

My client requires a Static IP for a SOAP/XML bank integration. Does this work with Drupal's SOAP Client?

For compatible Static requests, native PHP SoapClient documents separate proxy_host, proxy_port, proxy_login, and proxy_password options. Credentials belong in the login and password options, not the host or port.

Native SOAP does not inherit CMS HTTP settings, and these constructor options are not a documented Shield HTTPS-proxy recipe.

For Shield, assess a compatible cURL-backed SOAP integration.

Include WSDL and import retrieval as well as service calls, retain TLS verification, and configure appropriate timeouts.

Does this work with Pantheon's "Upstreams"?

Yes, configuration code can be distributed through an upstream.

Keep actual proxy credentials in Pantheon Secrets and retrieve the correct environment’s value at runtime. Do not commit credentials with the shared code.

Each consuming site still needs compatible clients and its own destination and bypass configuration.

Can I use QuotaGuard in my Quicksilver hooks (deploy scripts)?

Use Quicksilver hooks to notify Jira or trigger Jenkins when those endpoints require an allowlisted source IP. A deployment script can use QuotaGuard when its actual HTTP client supports the selected proxy route.

Retrieve runtime secrets with web scope through Pantheon’s documented PHP mechanism rather than embedding credentials in the script.

Configure the script’s client explicitly; website HTTP proxy settings do not establish that a deployment script has inherited the proxy configuration.

Review the execution context and destination before adopting the recipe.

Do I need a Pantheon "Enterprise" plan to use QuotaGuard?

No—you do not need Pantheon’s Secure Integration add-on simply to use QuotaGuard. QuotaGuard offers self-service setup for compatible application clients, so your team can configure a proxy route without asking Pantheon to provision each external service.

Check the runtime features and client requirements for your site; do not assume a particular plan name guarantees every transport.

Pantheon’s own Secure Integration is a separate, per-resource managed tunnel with eligibility and setup handled by Pantheon.

Ask Pantheon about current availability if that is the better route for your resource.

Still have questions?

We don’t outsource Support to non-Engineers.

Reach out directly to the Engineers who built Shield to discuss your specific architecture, integration challenges, or compliance constraints here 👇

🚀 Ready to Get Started? Choose Your QuotaGuard Path

QuotaGuard STATIC

Why: You need stable source IPs for general API access, AI workflows, or standard third-party integrations using compatible clients.
Best For: Developers, startups, and general application connectivity when an HTTP-proxy route meets your requirements.
Key Feature: HTTP proxy support, plus SOCKS5 for clients that explicitly support it. HTTPS requests retain destination TLS; the application-to-proxy hop is not separately TLS-encrypted by Static.
Sign Up for QG Static for Pantheon

QuotaGuard SHIELD

Why: You need TLS on the application-to-proxy hop as well as HTTPS to the destination.
Best For: Financial services, healthcare, and other sensitive-data integrations with a compatible HTTPS-proxy client and appropriate security controls.
Key Feature: An HTTPS proxy hop while preserving destination TLS without decrypting the outbound HTTPS payload. Shield supports your security design; the proxy alone does not establish HIPAA, PCI, or other compliance.
Sign Up for QG Shield for Pantheon

Trusted by Engineering Teams Everywhere

What our customers say

Customer experiences, in their own words. Swipe or scroll to read more.

We've been using QuotaGuard Static for nearly six years to provide static IP addresses to our clients so they are able to whitelist our network traffic.

Read full testimonial

We've been using QuotaGuard Static for nearly six years to provide static IP addresses to our clients so they are able to whitelist our network traffic.

The service has been hassle free, has never "not worked" or had any downtime to my knowledge. The only time we've reached out to support was during a migration from one cloud provider to another to ensure that we wouldn't cause interruptions in the service ourselves. The service we received at that time was prompt and professional.

Zach ColonVP of Engineering at ItsaCheckmate.comSubmitted Oct 20, 2023

The app's backend runs on serverless functions, and the railway data provider I was using only accepted requests from a fixed IP address. QuotaGuard gave me exactly that, and my passengers' PNR status checks kept working.

Read full testimonial

I used QuotaGuard Static IPs for ClearBerth, my train app for Indian Railways passengers. The app's backend runs on serverless functions, and the railway data provider I was using only accepted requests from a fixed IP address. QuotaGuard gave me exactly that, and my passengers' PNR status checks kept working.

It helped me because I could keep building the app without worrying about how to get a static IP. For a solo developer that is a real relief.

The best thing about QuotaGuard is the owner himself. Michael is kind, thoughtful and genuinely warm. When I wrote to say thank you, he replied personally, said it made his Sunday morning, and offered a returning customer discount for any future project. You do not often get that from a service company. I would happily use QuotaGuard again and I recommend it to any developer who needs a static IP.

Aditya Bhattacharya, ClearBerth

Aditya BhattacharyaFounder of ClearBerth appSubmitted Oct 18, 2026

QuotaGuard provided a static IP address via a SOCKS5 proxy. Setting up the proxy and using it from my server was very straightforward.

Read full testimonial

I have a web app running in Heroku, and that server occasionally needs to FTP files from another host. That host required requests to come from a whitelisted IP address. QuotaGuard provided a static IP address via a SOCKS5 proxy. Setting up the proxy and using it from my server was very straightforward.

Stephen BeitzelCTO, Narrative TechnologiesSubmitted Mar 28, 2024

I use QuotaGuard to connect with various APIs that require IP whitelisting and run web automations that require a country-specific IP. The stability and reliability of the service have been nothing short of exceptional.

Read full testimonial

I use QuotaGuard to connect with various APIs that require IP whitelisting and run web automations that require a country-specific IP. The stability and reliability of the service have been nothing short of exceptional. It simply works as expected and whenever I’ve had any questions Michael and the team are always very quick to respond to emails. I would recommend them without a doubt.

Jose VilchesCEO at SIM StoreSubmitted Oct 29, 2023

QuotaGuard has been a reliable partner for us for many years. Their service has consistently been solid, and when we ran into a more unusual use case, their team understood the situation quickly and worked closely with us to resolve the issues.

Read full testimonial

QuotaGuard has been a reliable partner for us for many years. Their service has consistently been solid, and when we ran into a more unusual use case, their team understood the situation quickly and worked closely with us to resolve the issues. That level of responsiveness and support has made a real difference for us.

Anton Litvinenkoco-founder @ Import2Submitted Aug 11, 2026

QG helped us prove our pipeline and workflow with users and in the end, we would have stayed but we use AWS for all our production so we had to switch. Sorry to go but loved every minute of it!

Read full testimonial

QUOTAGUARD FTW! We used qg for spooling up a prototype that needed access to MongoDB through Heroku without having to use 0.0.0.0 in mdb whitelist. Big nono for privacy and security. QG helped as we were able to add it as a resource in Heroku and test our prototype. As the platform matured, more test users came on board and our bandwidth scaled to a point where we were no longer a prototype so we moved over to AWS which is where our production apps live. The team at QG is beyond awesome. I sent an email and I think within 24hrs or less we had solved the issues with Tim and Michael. The fact they didn't pester after signup was refreshing as well. They are Dev dev's who get it. QG helped us prove our pipeline and workflow with users and in the end, we would have stayed but we use AWS for all our production so we had to switch. Sorry to go but loved every minute of it!

Greg LuttonCEO Exsurgo TechnologiesSubmitted Jun 1, 2026

Even though the issue was bank related, Michael and Randall provided exceptional support and helped me troubleshoot the issue.

Read full testimonial

I've had a issue tunneling requests to my bank's VPOS through QuotaGuard.

Even though the issue was bank related, Michael and Randall provided exceptional support and helped me troubleshoot the issue.

5 stars service, highly recommended!

Ozgur S.FounderSubmitted Jul 21, 2026

The product works great - but where they really shine is the exceptional customer service.

Read full testimonial

I needed to configure a static IP address for my app running on Heroku, so I could connect to an external database in a more secure manner. A colleague recommended Quotaguard as an option.

The product works great - but where they really shine is the exceptional customer service. One of my background workers was sneakily polling, which didnt show on the logs, and the Quotaguard support team showed patience and knowledge helping me get to the root of the problem. Fantastic team.

AlexSubmitted Aug 1, 2024

QuotaGuard is an excellent company to work with, they really helped me out on my API issue. Appreciate them as a partner.

Read full testimonial

QuotaGuard is an excellent company to work with, they really helped me out on my API issue. Appreciate them as a partner.

John William MeyerCEO, Jump FinanceSubmitted Sep 30, 2026

Solid service. :) Does what's on the tin.

Read full testimonial

Solid service. :) Does what's on the tin. They know what they're doing, and I mean that in two ways: (1) their execution of their value offering is *solid*, and (2) they appear undistracted by things that *aren't* what they're doing. A "small, sharp tools", you know?

IsaacLightwardSubmitted Jan 25, 2024

Reliability Engineered for the Modern Cloud

For over a decade, QuotaGuard has provided reliable, high-performance static IP and proxy solutions for cloud environments like Heroku, Kubernetes, and AWS.

Get the fixed identity and security your application needs today.